Your company's context. Your boundaries.
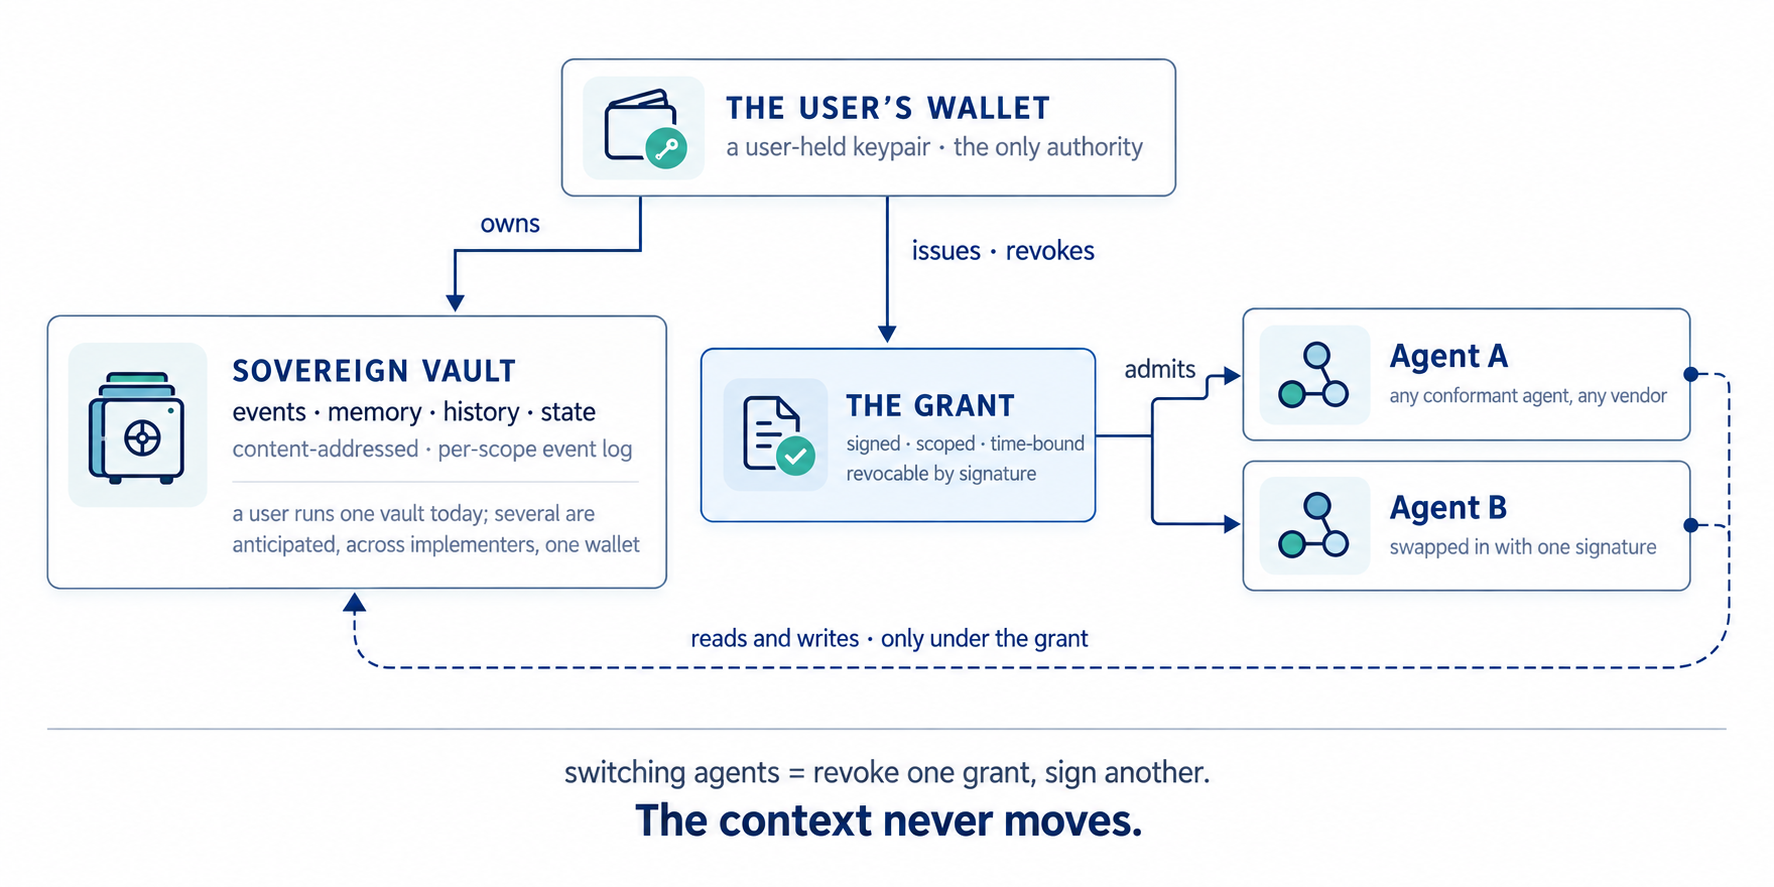
People and agents need useful context to work together. Your company decides who can use it, for what purpose, and when that access ends. The Agent OS is the reference implementation of SSCP, the Self-Sovereign Context Protocol, an open standard for owned, revocable, auditable context. SSCP describes the principles; the Agent OS brings them into company work.
The owner's key is the only authority
No platform-managed identity, even where it would simplify onboarding. Every alternative ends with a service owning the customer.
Permissions are cryptographic
No bearer tokens whose validity depends on a central issuer staying in service. A permission is a signed agreement between the owner's key and the agent's key.
Multi-implementer by design
Implementers compete on quality and economics, never on owning the customer.
Storage neutral
Content-addressed semantics are mandated. The storage layer is not.
Verifiable trajectory
Nothing is asserted as a feature before it ships in code.
Today's guarantee
Your context is owned and revocable, enforced by the runtime and recorded in the log.